

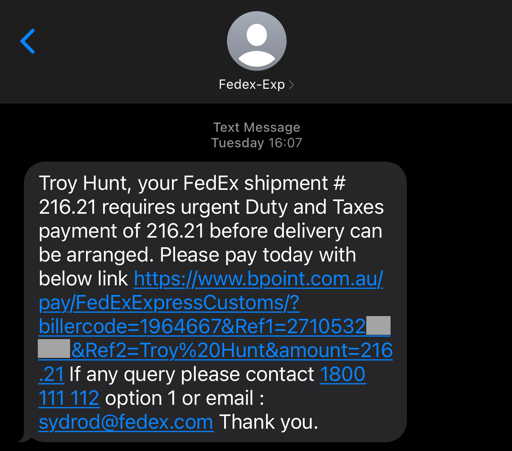
From 2024, but funny to read…
What makes this situation so ridiculous is that while we’re all watching for scammers attempting to imitate legitimate organisations, FedEx is out there imitating scammers!
From 2024, but funny to read…
What makes this situation so ridiculous is that while we’re all watching for scammers attempting to imitate legitimate organisations, FedEx is out there imitating scammers!
The head of my IT department once asked me to send him an AWS root password over email because there was an issue with billing on the account.
Another manager told users to just bypass the certificate errors on a new web service.
Multiple times I’ve had people tell me over teams to do all kinds of weird things to work around security errors.
It’s a weird thing where people in IT think the security rules are for everyone else and not for them. And it’s just laziness. I wind up doing all of the work to set everything up so the user is going to subdomain.[my company’s domain] and the cert is valid and if it’s an internal service, use kerberos to validate the user so they don’t even enter a password.
The goal should always be that the user sees zero red flags when using a service. But a lot of people are too lazy to implement what’s needed so eliminate all of those red flags and instead just send out a message to tell people to ignore them.
Yeah, there were two IT techs at one company who routinely asked for user passwords, in part because some of the software we used require setup in the user account. I’d say no, but I was on a few reply all emails where others provided their password to everyone on the email.
I forwarded those emails after the IT manager after the company email server got blacklisted by a client for our emails being used as an attack vector to phish.