

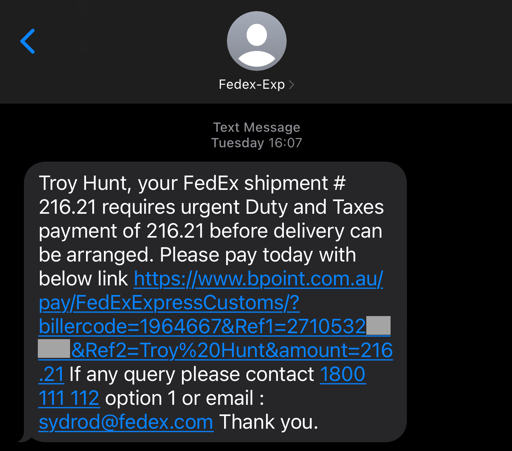
From 2024, but funny to read…
What makes this situation so ridiculous is that while we’re all watching for scammers attempting to imitate legitimate organisations, FedEx is out there imitating scammers!
From 2024, but funny to read…
What makes this situation so ridiculous is that while we’re all watching for scammers attempting to imitate legitimate organisations, FedEx is out there imitating scammers!
Now the spamer has confirmation that this email address is active, can be shared in their network.
Edit: email address
The known legit website, not the one in the link.
You don’t use the link. You go to the website by your normal means. In this case, he opened a browser and went to the FedEx site on his own. That way you know you are on the real site.
Never thought about it that way, I usually open sketchy stuff in tor
If you remove the tracking parts of the URL.
Remember kids, everything after the ? In a URL is unnecessary tracking! Trim your URLs before sharing!
Depends entirely on the site. Amazon? Sure.
Many other sites will put query information in this part of the URL, so all you’re doing is removing the information you put in the previous page and probably invalidating your search results
Not necessarily, or even usually.