
4·
5 hours agoeven a very similar logo …
Former account: @[email protected]
Keyoxide: aspe:keyoxide.org:KI5WYVI3WGWSIGMOKOOOGF4JAE (think PGP key)
even a very similar logo …
First, @[email protected] was right, the background by itself without the box has a synthid, I commented some screenshots below.
I also see those “ai artifacts” on the barcode, though I wasn’t as sure about it before seeing the synthid.
I can make out that the lines don’t run quite parallel but form these V and Λ shapes, closer together on one end and merging together.
Counting the left most blurry line as one, the 5th is leaning into the 4th line at the top for example. The compression is strong and the image doesn’t have enough resolution to make it out very clearly, but it still looks like an actual detail not a compression artifact to me. The lines are all a bit wonky, more than the noise could do.
Here’s a way more obvious example:
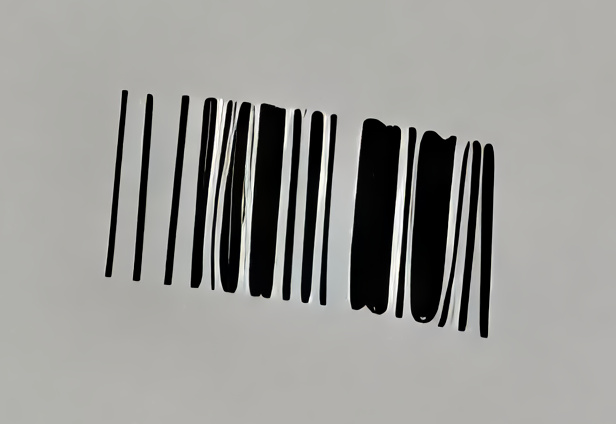
This has some other artifacts too that I don’t see in the post, but you can see the general wonkiness. And also how some lines have “bled” together, though this isn’t a great example of that.

This seems to be from a dedicated joke wiki not wikipedia. Mediawiki is a software anyone can set up.
I think this is the 1990th comic by extra fabulous comics (or smthn) not from the year 1990. EFC started in 2011.
Can’t believe people made comics like that in 1990.

You put an account id/token into dns, which allows machines to renew the cert under that account with just the account credentials (key).
So after setting it up, the token stays the same forever and you don’t need to touch dns.
Such tokens are already used by acme clients when they renew their certs. It’s also how acme providers can detect expiring certificates for example.
I find it a bit weird, since the whole deal of shortening lifetimes was in part to protect against stolen certificates, and now by stealing the account key you are again stealing the ability to indefinitely make certificates.
At least you can “revoke” such access by switching the account and updating the dns record authorizing it.